
ISO 9001 certification shows your customers, buyers and tender authorities that your organization runs on a quality management system (QMS) that has been independently audited against an international standard. It shows that you can consistently deliver products and services that meet customer and regulatory requirements, and that you keep improving how you work.
Guardian Assessment Private Limited is an independent certification body accredited by the United Accreditation Foundation (UAF) and the International Accreditation Service (IAS). We audit organizations globally against ISO 9001 and issue certificates when the requirements are met. This page covers everything you need to know before applying: who can get certified, what the standard requires, which documents you need, how the certification process works, what affects the cost, and how to verify a certificate.
ISO 9001 Certification at a Glance
Question | Quick Answer |
What is ISO 9001? | An international standard for Quality Management Systems (QMS). |
Who can apply? | Organizations of any size and sector, including MSMEs, manufacturers, and service providers. |
Current edition | ISO 9001:2026, published on 16 September 2026. |
Who issues certificates? | Independent certification bodies, not ISO itself. |
What is the certification process? | Application review, audit planning, Stage 1, Stage 2, independent review, and certification decision. |
How long is certification valid? | Normally a three-year certification cycle, subject to surveillance and continued conformity. |
How much does certification cost? | Depends on employee numbers, locations, scope, complexity, and audit requirements. |
How can you apply? | Submit your organization’s details and proposed certification scope for review and quotation. |
Certification is not automatic after submitting an application or completing an audit. The organization must demonstrate conformity with the applicable requirements, and certification is granted only following a positive certification decision.
What Is ISO 9001 Certification?
ISO 9001 is an international standard that specifies requirements for a Quality Management System. It helps organizations establish consistent processes, understand customer needs, manage risks and opportunities, evaluate performance, and continually improve the way they operate.
A quality management system is more than a collection of documents. It includes the responsibilities, processes, resources, and records an organization uses to plan, deliver, monitor, and improve its products or services.
For example, a manufacturer may use its QMS to check incoming materials, control production, inspect finished products and investigate customer complaints. A service provider may use it to review client requirements, assign responsibilities, monitor service delivery and resolve recurring issues.
ISO 9001 provides a common framework rather than prescribing one fixed method of operation. The system should reflect the organization’s size, activities, risks, customer expectations, and applicable requirements.
What Is the Difference Between ISO and a Certification Body?
Three parties have distinct responsibilities:
- ISO (International Organization for Standardization): Develops and publishes international standards. ISO does not audit individual businesses or issue ISO 9001 certificates.
- Your organization: Establishes, implements, maintains, and improves a quality management system that meets the applicable requirements.
- The certification body: Independently audits the management system and makes a certification decision based on objective evidence and applicable certification requirements.
ISO 9001 certification applies to the organization’s management system and the activities covered by its certification scope. It does not mean that ISO has directly certified the organization or that every product or service is guaranteed to be defect-free
Request Quotation
Other Standards
Recognition
Sample Certificate
Who Can Apply for ISO 9001 Certification?
ISO 9001 can be applied for by organizations of all sizes and across different sectors. Small businesses, MSMEs, startups, established enterprises, and large organizations can all seek certification. Organizations commonly pursue ISO 9001 certification for:
- Government tenders: Some government departments, public sector undertakings (PSUs), and Government e-Marketplace (GeM) procurement categories include ISO 9001 certification in their eligibility requirements.
- Buyer and supplier requirements: Large companies and multinational organizations may require their suppliers to hold an appropriate ISO 9001 certificate.
- Export opportunities: International customers may ask for accredited ISO 9001 certification when assessing suppliers.
- Business improvement: Organizations use ISO 9001 to improve process control, establish responsibilities, and maintain consistency as they grow.
Which Industries Can Get ISO 9001 Certified?
ISO 9001 is suitable for a wide range of industries, including:
- Manufacturing and engineering: Managing production, inspections, suppliers, and product conformity.
- Construction and contracting: Controlling project requirements, materials, subcontractors, and work inspections.
- IT and software services: Managing client requirements, service delivery, project reviews, and customer feedback.
- Healthcare: Supporting consistent processes relevant to the organization’s activities and certification scope.
- Education and training: Establishing consistent processes for educational and administrative services.
- Food processing and distribution: Managing operational processes, product controls and customer requirements.
- Trading and logistics: Managing orders, suppliers, storage, dispatch and customer complaints.
- Consulting and professional services: Managing deliverables, responsibilities, customer communication and service performance.
The requirements are applied according to the organization’s actual operations. A small consultancy, for example, will not need the same operational controls as a multi-location manufacturing company.
What Should You Have in Place Before Certification?
Before undergoing the certification audit, your organization should be able to demonstrate that its QMS is operating effectively and addresses the applicable requirements. Preparation normally includes:
- A clearly defined QMS scope covering relevant activities and locations.
- A quality policy and measurable quality objectives.
- Defined processes, responsibilities, and operational controls.
- Appropriate documented information and records.
- Employees with the competence and awareness needed for their responsibilities.
- Completed internal audit and management review activities as required for certification readiness.
- Processes for identifying nonconformities and taking corrective action.
- An understanding of applicable customer, statutory, and regulatory requirements.
The purpose is not simply to prepare documents for an auditor. Your organization should demonstrate that its management system is implemented and followed in everyday operations.
Benefits of ISO 9001 Certification
The value of ISO 9001 comes from both the independent assessment of the management system and the operational improvements that an effectively implemented QMS can support.
1. Support Tender and Supplier Requirements: Certain government tenders, public sector procurement processes and corporate supplier programs specify ISO 9001 certification as an eligibility condition. Certification may help an organization meet these requirements, provided its certificate satisfies the relevant conditions concerning scope, accreditation, standard edition, and validity.
2. Build Customer Confidence: ISO 9001 certification provides evidence that an organization’s quality management system has been independently assessed against recognized requirements. This can help customers and buyers evaluate whether a supplier has established processes for managing quality and meeting agreed requirements.
3. Improve Consistency: Defined processes, clear responsibilities, and appropriate controls can reduce variation in how work is performed. This can help organizations deliver more consistent products and services across different orders, projects, teams, and operating locations.
4. Identify and Address Problems: Monitoring processes, reviewing results, and investigating complaints can help organizations identify recurring issues, understand their causes, and take corrective action.
5. Improve Operational Efficiency: Reviewing how activities are performed can reveal unnecessary delays, duplicated effort, unclear responsibilities, and inefficient use of resources. Addressing these issues can improve coordination and operational performance.
6. Support Better Decisions: Performance data, customer feedback, internal audit findings, and management review results help organizations make decisions based on evidence rather than assumptions.
7. Encourage Continual Improvement: ISO 9001 provides a structured approach to evaluating performance, addressing nonconformities, and identifying opportunities to improve the management system over time.
What Do These Benefits Look Like in Practice?
- Manufacturing and Engineering: A manufacturer receives repeated complaints about products that do not meet customer specifications. By reviewing inspection records, production methods, and defect causes, the company can identify where controls need improvement and reduce the likelihood of similar problems recurring.
- Construction and Contracting: A contractor must manage project requirements, materials, subcontractors, and inspection records. Defined processes clarify who checks materials, how changes are communicated, and how completed work is reviewed before acceptance.
- IT and Software Services: An IT service provider experiences missed deadlines and unclear handovers between teams. Structured processes for reviewing requirements, assigning work, checking deliverables, and managing feedback can support more consistent service delivery.
- Trading and Distribution: A trading business experiences errors in orders and deliveries. Controls for order verification, supplier evaluation, dispatch checks, and complaint handling can help identify recurring mistakes and improve coordination.
These examples illustrate how a QMS may be used. The actual benefits depend on how effectively the organization implements and maintains its processes.
ISO 9001 Requirements: Clauses 4 to 10
The principal auditable requirements of ISO 9001 are contained in Clauses 4 to 10. These cover the organization’s operating environment, leadership, planning, resources, operations, performance evaluation, and improvement.
Clause | Requirement Area | What It Covers |
4 | Context of the Organization | Relevant internal and external issues, interested parties, QMS scope and processes. |
5 | Leadership | Management commitment, customer focus, quality policy, responsibilities, accountability and quality culture. |
6 | Planning | Determining and addressing risks and opportunities, establishing quality objectives and planning changes. |
7 | Support | Resources, competence, awareness, communication and documented information. |
8 | Operation | Planning and controlling activities related to products and services, including suppliers, design where applicable, delivery and nonconforming outputs. |
9 | Performance Evaluation | Monitoring, measurement, customer satisfaction, internal audits and management reviews. |
10 | Improvement | Nonconformities, corrective action and continual improvement. |
Organizations must apply the requirements relevant to their activities, scope and circumstances. An authorized copy of the applicable ISO 9001 edition should be used to establish or evaluate a management system. This guide provides an overview and does not replace the standard.
How Are ISO 9001 Requirements Checked During an Audit?
An ISO 9001 auditor does not assess a management system by examining documents alone. The audit also evaluates whether established processes are implemented and working as intended. Depending on the organization’s certification scope, an auditor may:
- Review how customer requirements are received, understood and confirmed.
- Ask employees to explain the processes relevant to their responsibilities.
- Examine production, inspection, monitoring or service delivery records.
- Evaluate how suppliers are selected and monitored.
- Check how complaints, errors and nonconforming outputs are handled.
- Review internal audit findings, management reviews and corrective actions.
- Observe activities to determine whether actual practices are consistent with established processes.
For example, if a manufacturing company has a procedure for inspecting finished products, the auditor may review inspection records and ask relevant employees to explain how the checks are performed. The objective is to gather sufficient evidence that the QMS conforms to the applicable requirements and operates effectively.
Documents and Records Required for ISO 9001 Certification
ISO 9001 uses the term documented information to describe information an organization maintains and records it retains as evidence. The documentation needed depends on the organization’s activities, processes, complexity and the applicable edition of ISO 9001.
Common Documents to Maintain some examples include:
- Quality Management System scope.
- Quality policy and quality objectives.
- Process descriptions, procedures or work instructions where necessary.
- Criteria for evaluating and selecting external providers.
- Other documented information needed to operate and control processes effectively.
Common Records to Keep
Depending on the organization’s activities, relevant records may include:
- Employee competence, qualifications and training evidence.
- Calibration or verification records for monitoring and measuring equipment, where applicable.
- Reviews of customer, product and service requirements.
- Design and development records, where applicable.
- Supplier evaluation and re-evaluation results.
- Monitoring, measurement, inspection and conformity records.
- Records relating to nonconforming outputs.
- Internal audit programme and results.
- Management review outputs.
- Nonconformities and corrective actions.
This is a practical overview, not an exhaustive list of every documented-information requirement. The organization must maintain and retain the information required by the applicable standard and needed for effective process operation.
Is a Quality Manual Mandatory?
ISO 9001 does not generally require a separate document titled “Quality Manual.” Organizations may choose to maintain one if it helps explain their management system, processes, and responsibilities. The important requirement is to maintain the necessary documented information and demonstrate that the management system works in practice. For application documents and related forms, visit the Guardian Downloads page.
Guardian's ISO 9001 Certification Process
Guardian Assessment follows a structured management system certification process aligned with ISO/IEC 17021-1 and applicable accreditation requirements. The initial certification process consists of six main stages.
Step 1: Application Review: Submit information about your organization, business activities, employee numbers, operating locations, and proposed certification scope. Guardian reviews the application to understand your certification requirements, assess the proposed scope, and determine whether the requested activities fall within its capabilities and applicable accreditation arrangements.
Step 2: Audit Planning: After the application review, Guardian determines the required audit duration, appoints a competent audit team, and establishes the audit plan. Planning considers factors such as workforce size, operating shifts, locations, process complexity, and the activities included within the proposed certification scope.
Step 3: Stage 1 Audit: The Stage 1 audit evaluates the organization’s readiness for the Stage 2 assessment. The auditor reviews relevant QMS documented information, scope, processes, and implementation status, including the status of internal audits and management reviews. The findings help determine whether the organization is sufficiently prepared to proceed.
Step 4: Stage 2 Audit: The Stage 2 audit evaluates the implementation and effectiveness of the Quality Management System. Auditors gather objective evidence through interviews, observation of activities, examination of records, and sampling of relevant processes. The assessment determines whether the management system conforms to the applicable ISO 9001 requirements and can achieve its intended results.
Step 5: Audit Findings and Independent Technical Review: If nonconformities are identified, they are reported to the organization. The organization is responsible for investigating the causes, carrying out appropriate corrections and corrective actions, and submitting the required evidence. Guardian evaluates the relevant evidence according to the applicable certification requirements. Audit findings and certification information then undergo independent technical review by appropriately authorized personnel who were not involved in conducting the audit.
Step 6: Certification Decision and Certificate Issuance: An independent certification decision is made after the required audit activities and review have been completed. If the applicable requirements are satisfied and the certification decision is positive, Guardian issues the ISO 9001 certificate identifying the certified organization, approved scope, locations, and applicable standard edition. Completing an application or certification audit does not guarantee that a certificate will be issued.
What Happens After Certification?
ISO 9001 certification involves ongoing assessment rather than a one-time audit.
- ISO Surveillance audit: Conducted during the certification cycle to evaluate continued conformity with the applicable requirements.
- ISO Recertification audit: Conducted before the certification cycle ends to assess whether certification can continue into a new cycle.
The certified organization remains responsible for maintaining and improving its QMS throughout the certification period. Request ISO 9001 Certification
How Long Does ISO 9001 Certification Take?
The time required for ISO 9001 certification varies according to the organization’s readiness, activities, and audit requirements. Important factors include:
- Implementation status of the QMS.
- Organization size and number of employees.
- Number of sites and operating locations.
- Complexity of processes, products, and services.
- Availability of documented information and audit evidence.
- Audit scheduling and planning.
- Time required to address nonconformities.
A business with an established and effectively operating QMS may be ready for certification assessment sooner than an organization that is still developing its processes. There is no single completion period that applies to every organization. Guardian can discuss the expected audit arrangements after reviewing the relevant application information.
How Long Is an ISO 9001 Certificate Valid?
ISO 9001 certification normally follows a three-year certification cycle, subject to continued conformity and successful completion of required surveillance activities. ISO Surveillance audits are normally conducted annually during the certification cycle. Before the cycle ends, a recertification audit and positive certification decision are required for certification to continue. Certification may be suspended or withdrawn if the organization fails to meet the applicable certification requirements. Organizations holding certificates to a superseded edition must also consider any applicable transition deadline.
What is The Cost of ISO 9001 Certification
There is no universal fixed price for ISO 9001 certification because audit requirements differ from one organization to another. Certification cost depends primarily on the audit effort, duration, and resources needed to assess the organization’s management system.
Factors That Affect Certification Cost
Factor | How It Affects Cost |
Number of employees | Influences audit duration under applicable certification rules. |
Number of locations | Multiple sites may require additional audit activities. |
Certification scope | The activities and processes covered affect assessment requirements. |
Process complexity | Complex operations may require additional audit effort or technical competence. |
Operating shifts | Different shifts may need to be considered during audit planning. |
Travel requirements | Auditor travel and accommodation may affect the quotation. |
What Should an ISO 9001 Certification Quote Include?
When comparing quotations, organizations should understand the costs associated with the initial certification and ongoing certification cycle.
- Initial certification: Includes the applicable application review, audit planning, Stage 1 and Stage 2 audits, technical review, and certification decision activities.
- Surveillance audits: Periodic surveillance audits involve further assessment activities and applicable fees during the certification cycle.
- Recertification: A recertification audit is required before the end of the cycle for continued certification. Its cost should be considered separately when planning future certification expenses.
The internal cost of establishing and maintaining a QMS is separate from the certification body’s audit fees. Organizations should review the complete certification quotation and relevant terms rather than comparing only the initial audit price.
What Information Is Needed for a Quote?
To request an ISO 9001 certification quotation, provide:
- Legal organization name and contact information.
- Main business activities, products and services.
- Proposed certification scope.
- Number of employees and operating shifts.
- Number and locations of sites.
- Existing certification details, if any.
- Specific customer, tender or accreditation requirements, where relevant.
Guardian reviews the information to determine the applicable certification arrangements and quotation. Get Your ISO 9001 Certification Quote You can also obtain the relevant Inquiry Form from our Downloads page.
Which Edition of ISO 9001 Applies Now?
ISO 9001:2026 is the current edition of the international Quality Management System standard. It was published on 16 September 2026 and replaces ISO 9001:2015. The revised edition builds on the established quality management framework, with greater emphasis on leadership, quality culture, ethical behaviour and clearer treatment of risks and opportunities. Organizations holding ISO 9001:2015 certificates have a transition period to move to the revised edition.
Important Transition Dates
Date | Requirement |
31 March 2028 | New and initial accredited ISO 9001 certifications may only be issued to the 2026 edition under the applicable transition arrangements. |
30 September 2029 | Existing ISO 9001:2015 certifications must complete their transition to ISO 9001:2026. |
Existing certificates remain subject to their individual expiry dates, surveillance requirements, and certification status. Organizations already certified to ISO 9001:2015 should review the revised requirements and plan their transition with their certification body. A transition audit may be combined with a scheduled surveillance or recertification audit or conducted separately. First-time applicants should confirm which edition their certification body is currently accredited and authorized to issue.
Guardian will confirm the applicable standard edition and certification arrangements during application review. For further details:
Accredited ISO 9001 Certification and Certificate Verification
What Is the Difference Between Certification and Accreditation?
- Certification is the independent assessment of an organization’s Quality Management System against the applicable ISO 9001 requirements.
- Accreditation is the independent assessment of a certification body’s competence and impartiality for specified certification activities.
When selecting a certification body, organizations should confirm that its accreditation covers the relevant standard, edition, technical scope, and certification activity. Accreditation provides additional confidence in the certification process, but it does not automatically guarantee acceptance by every buyer, regulator, or tender authority.
How to Verify an ISO 9001 Certificate
Before relying on a certificate for supplier approval, government tenders, or other business requirements, check the following information.
- Verify the issuing certification body: Use the certification body’s official verification system to check available certificate details and current status. Guardian certificates can be checked through the Guardian Certificate Search.
- Check the accreditation scope: Review the relevant accreditation body’s official records to confirm the certification body’s accreditation status and scope. Guardian’s accreditation information can be checked through:
- United Accreditation Foundation (UAF)
- International Accreditation Service (IAS) You can also review Guardian’s Accreditation Statement.
- Check IAF CertSearch, where applicable: IAF CertSearch provides information about accredited management system certifications where relevant records are available. If a certificate is not listed in a particular database, do not automatically assume that it is invalid. Confirm its status directly through the issuing certification body and relevant accreditation body.
What Should an ISO 9001 Certificate Show?
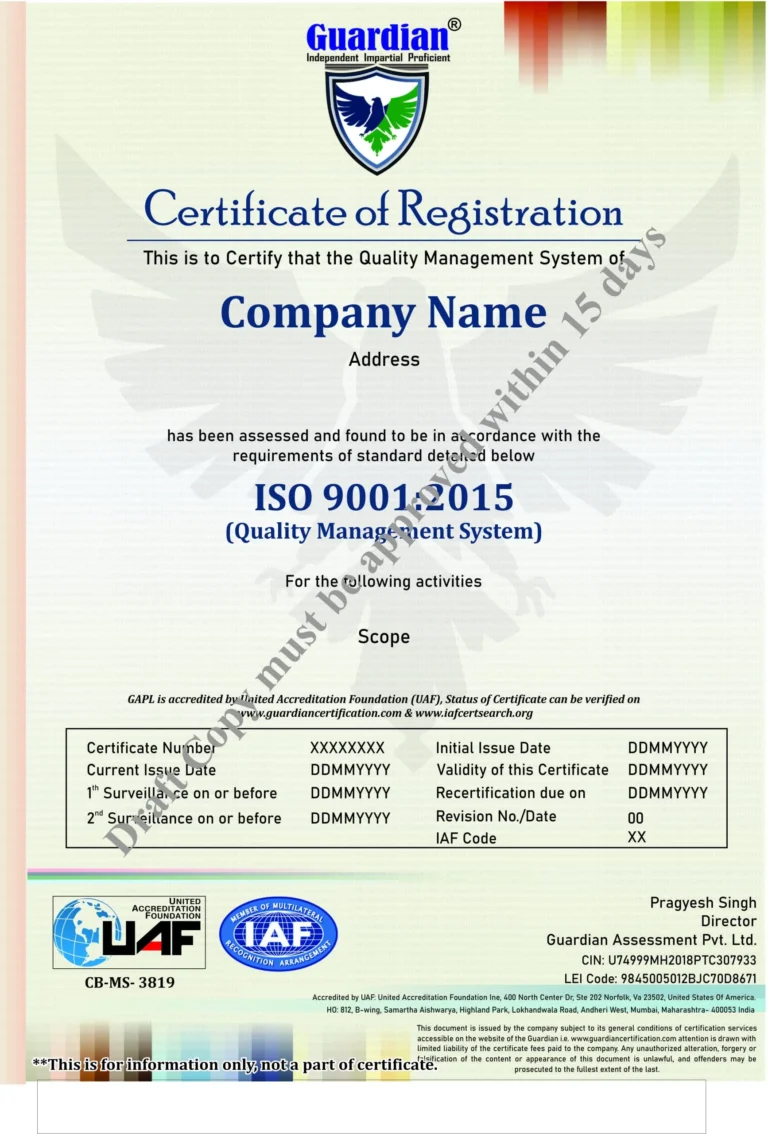
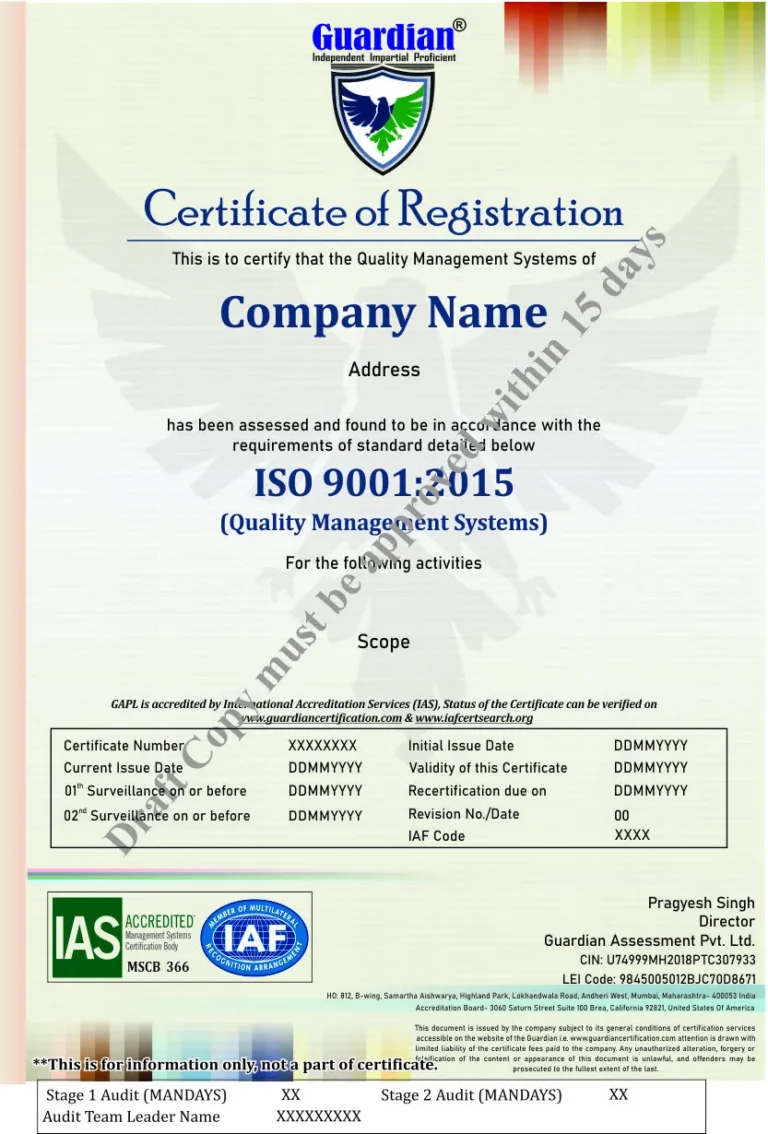
An ISO 9001 certificate normally identifies:
- The certified organization’s name.
- Relevant certified locations.
- Applicable ISO 9001 edition.
- Certification scope.
- Certificate number.
- Issue and expiry information.
- Issuing certification body.
- Applicable accreditation information.
Always confirm that the certificate’s scope, accreditation, standard edition, and current status meet the requirements of the organization that will rely on it.
Can ISO 9001 Be Integrated With Other ISO Standards?
Organizations may operate ISO 9001 alongside other management system standards when those standards are relevant to their activities. An Integrated Management System (IMS) helps coordinate compatible policies, responsibilities, processes, internal audits, and management reviews. This can reduce duplication and improve consistency across different management system activities.
ISO 9001 is commonly integrated with:
- ISO 14001: Environmental Management Systems.
- ISO 45001: Occupational Health and Safety Management Systems.
- ISO/IEC 27001: Information Security Management Systems.
- ISO 22000: Food Safety Management Systems.
- ISO/IEC 20000-1: Service Management Systems.
- ISO/IEC 27701: Privacy Information Management Systems.
- ISO/IEC 42001: Artificial Intelligence Management Systems.
Certification to one standard does not automatically demonstrate conformity with another. Each certification requires assessment against its applicable requirements. Organizations considering multiple standards should confirm the availability and accredited scope of each certification service before applying.
Why Choose Guardian Assessment for ISO 9001 Certification?
Guardian Assessment Private Limited is an independent management system certification body headquartered in Lucknow, Uttar Pradesh.
- UAF and IAS Accreditation: Accreditation applies to specified certification activities, subject to the approved scope and applicable requirements.
- Independent Certification: We maintain separation between certification, consultancy, and internal audits to support impartiality.
- Structured Process: Our process includes application review, Stage 1 and Stage 2 audits, technical review, certification decisions, and surveillance.
- Transparent Quotations: Audit duration and fees depend on your organization’s size, activities, locations and complexity.
- Services Across India: We serve eligible organizations across India, subject to scope and technical competence requirements.
- Multiple Standards and Transfers: Ask us about combined certification arrangements or transferring an existing accredited ISO 9001 certificate, subject to review.
Discuss Your ISO 9001 Certification Requirement
Frequently Asked Questions
No. ISO 9001 can be applied to service providers, IT companies, contractors, logistics businesses, educational organizations, healthcare providers, consultants, and many other sectors.
Common documented information includes the QMS scope, quality policy, quality objectives, relevant process information, supplier evaluation records, monitoring results, internal audit results, management review outputs, and corrective-action records. The exact requirements depend on the organization's activities and applicable standard.
The timeline depends on the organization's QMS readiness, size, complexity, number of locations, audit arrangements, and time required to resolve any nonconformities. There is no fixed completion period for every organization.
ISO 9001 certification normally follows a three-year cycle, subject to surveillance audits and continued conformity. Recertification is required to continue certification into a new cycle.
ISO 9001:2026 is the current edition. It was published on 16 September 2026 and replaces ISO 9001:2015.
Under the published transition requirements, organizations holding ISO 9001:2015 certification must complete their transition to ISO 9001:2026 by 30 September 2029, subject to any earlier certificate expiry or other applicable requirements.
You can begin your certification enquiry online by submitting your organization's details, activities, employee numbers, operating locations and proposed certification scope. Guardian can then review the information and explain the applicable application and audit arrangements.
An existing valid, accredited ISO 9001 certificate may be eligible for transfer, subject to review of its certification status, scope and applicable transfer requirements.